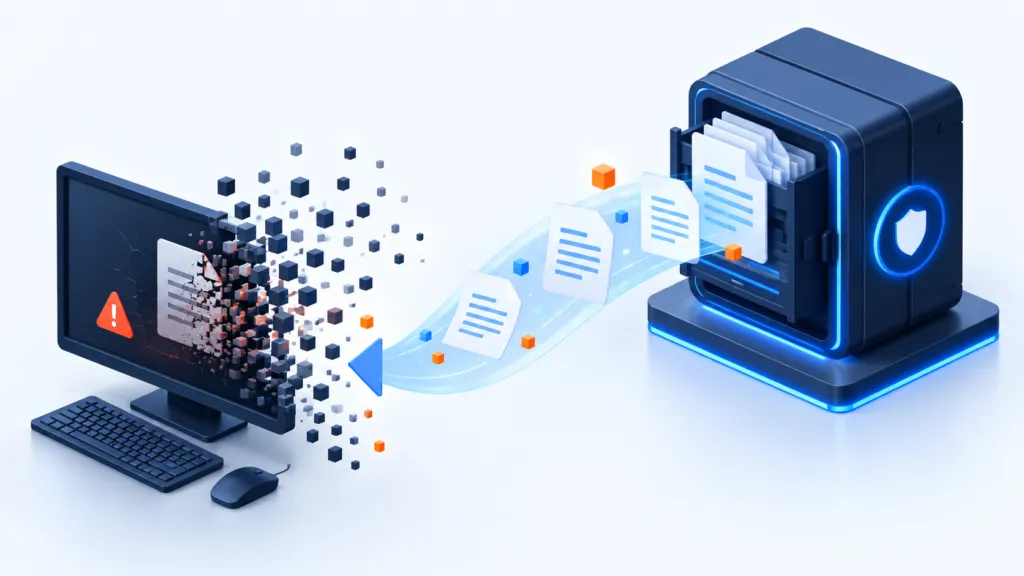
Not every attack demands money for a key. Wiper malware is designed to erase or disrupt data, sometimes also preventing the system from starting. The historical Meteor case highlights why preparation must cover losses that decryption cannot reverse.
Prepare for deletion too
- Detect and isolate
- Check a clean copy
- Recover and verify
Deletion is not ordinary encryption
When data is destroyed, do not rely on receiving a key from the attacker. Assess the data and build recovery around a valid, separate copy. Experimenting on an affected system may alter information needed for investigation.
Cover the system, not just documents
Restoring a service may require the operating system, settings, applications and working data. Record what is backed up and how to reinstall components outside the backup. Make sure startup tools and access to a recovery destination are available too.
Separate copies and permissions
If the same account can damage both the source and every copy, having copies alone is insufficient. Review deletion permissions, remote access and separated or protected copies. Retain more than one point in time to address damage discovered late.
Verify the return to work
After recovery, check applications, permissions and data with the system owners. Measure the time to restore service. Being able to copy files does not prove that an entire business process works again.
What should the exercise lead you to update?
- Coverage of missing data and settings.
- Access procedures for installation and recovery tools.
- Responsibility for approving a return to production.
- Backup history and integrity checks.
This is an adaptation of a historical case, not an alert about a currently active Meteor attack.