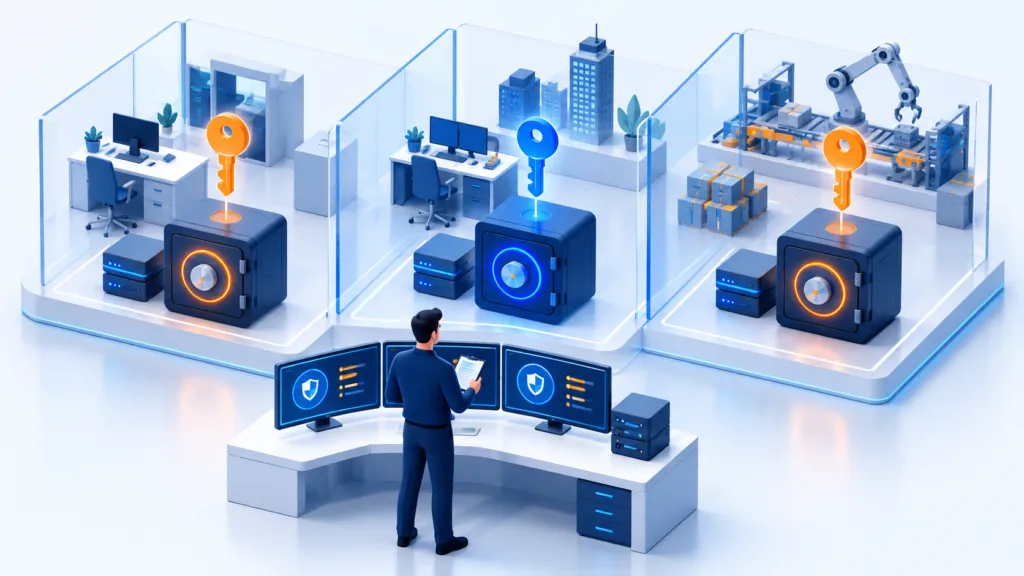
A service provider managing backups for several businesses holds sensitive information from different organizations. The goal is to work efficiently without turning one account or failure into an access path to every backup.
Clear boundaries between clients
- Separate permissions
- Protected destinations and keys
- Recovery tests for every client
Separate clients
Define each client’s own permission scope, backup destination and settings. Folder separation alone is insufficient if one account can read and delete everything. Check recovery, exports and reports too: an employee working with one client should not see another’s information.
Assign access by role
Distinguish viewing job status from changing policies and restoring data. Assign individual accounts and multi-factor authentication, and minimize administrative privileges. Emergency access should be documented, temporary and controlled, with a defined procedure when an employee is unavailable.
Protect copies and keys
Plan encryption, protection against modification or deletion and separate management accounts. Define who holds recovery keys and how they are used in an emergency. An encrypted copy is useless if its key is lost or permission to access it is unavailable.
Monitor and practise for every client
- Configure alerts for failures, permission changes and copy deletion.
- Test recovery against the client’s service objectives.
- Document onboarding, offboarding and removal of employee access.
- Report open exceptions as well as successful jobs.
Centralized management should make oversight easier. It does not replace testing client boundaries or responsibility for each client’s information.