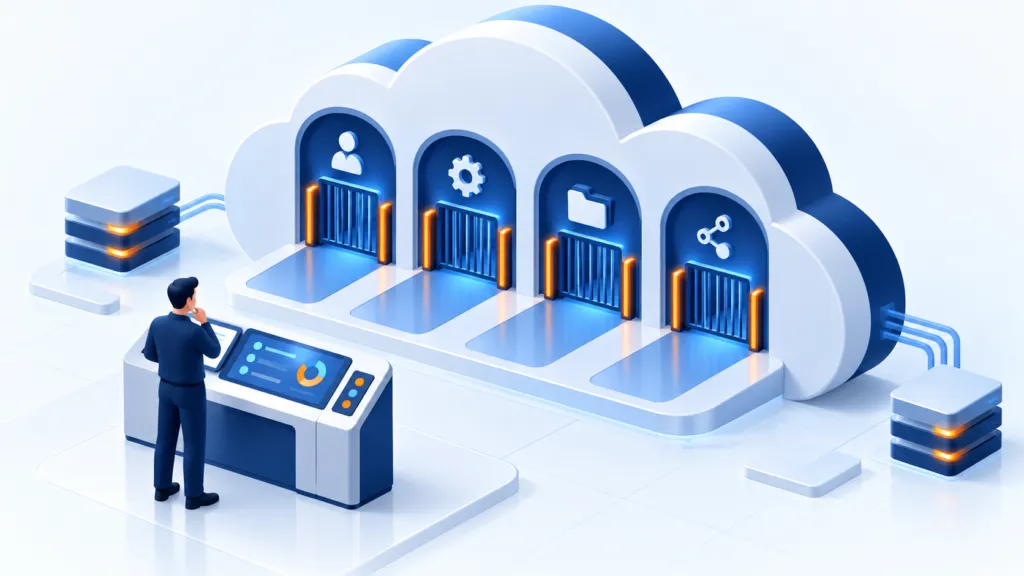
Moving to the cloud changes where people work and how access to information is granted. It does not transfer all security responsibility to the provider. Account settings, user permissions and file sharing still need management.
The cloud needs oversight
- Accounts and identities
- Sharing and permissions
- Alerts and a separate backup
Misconfiguration can expose information
Check which services are accessible externally and which repositories or folders are shared. Do not limit checks to the day of setup: a project change or temporary permission may leave access open over time.
Identities and permissions are critical
Give each user only the access required for their role. Use identifiable accounts and appropriate authentication, and review administrator accounts, service accounts and former employees. A broadly privileged service account needs attention even if nobody signs in to it manually.
File sharing needs oversight
Review public links, external sharing and permission expiry. Define who may share sensitive information and how access is revoked when work ends. Moving information to the cloud does not replace data classification.
Interfaces and automation require maintenance
API keys, which provide software access, need limited permissions and secure storage. Monitor unusual use, replace exposed credentials and update components. Do not store secrets in code or shared files.
Preserve the ability to recover
- Check who is responsible for backup and recovery in each service.
- Keep history and a suitable recovery path.
- Monitor changes to permissions and settings.
- Test alternative access if the primary account is unavailable.