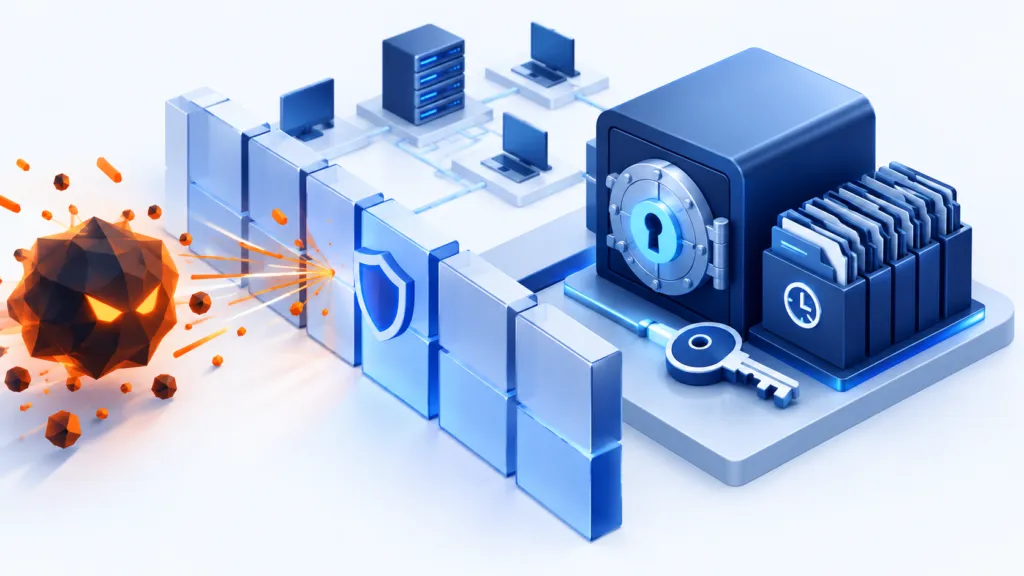
For backup to help during a ransomware incident, it must remain intact and accessible after the primary environment is compromised. Review the backup system’s own accounts, network paths and deletion permissions.
Protect the route back
- Separate management accounts
- Copies protected against damage
- Testing in a clean environment
Separate production from backup
Avoid giving users broad access to backup copies. Separate management accounts and access paths as needed, and test what can be done from a compromised computer. An additional copy in the same shared folder may be damaged along with the source.
Protect copies and policies
Consider a disconnected copy or protection against modification on storage that supports it. Check who can delete versions, change retention periods and replace keys. Protection depends on configuration; do not assume one setting blocks every scenario.
Keep sufficient history
An incident may be discovered after data has already been damaged. Longer history may help locate a clean recovery point, but you also need a way to test it. Choose retention according to risk and the rate of change.
Prepare a clean recovery path
Store recovery tools and access details securely. Test how to reach them if the identity system or administrator workstation is compromised. Restoring into an infected environment may bring the problem back; follow a coordinated response plan.
What should you practise?
- Recovery from a separate copy when the source is unavailable.
- Finding a version from before simulated damage.
- Using emergency permissions and keys.
- Receiving an alert about unusual deletion or modification.
Further reading: Ransomware response plan.